Search

Hongke's latest articles

HongKe

Lorem ipsum dolor sit amet, consectetur adipiscing elit. Ut elit tellus, luctus nec ullamcorper mattis, pulvinar dapibus leo.

From Reactive Defense to Proactive Prevention: Easy Risk Assessment and Auditing of Critical Infrastructure Ordinances with KnowBe4

With Hong KongProtection of Critical Infrastructure (Computer Systems) OrdinanceCISOs and risk managers are under pressure to comply with Section 24 (Annual Risk Assessment) and Section 25 (Bi-Annual Security Audit). The traditional "vulnerability scanning" assessment is no longer sufficient, because 80% Safety Incidents Caused by Human FactorsThe

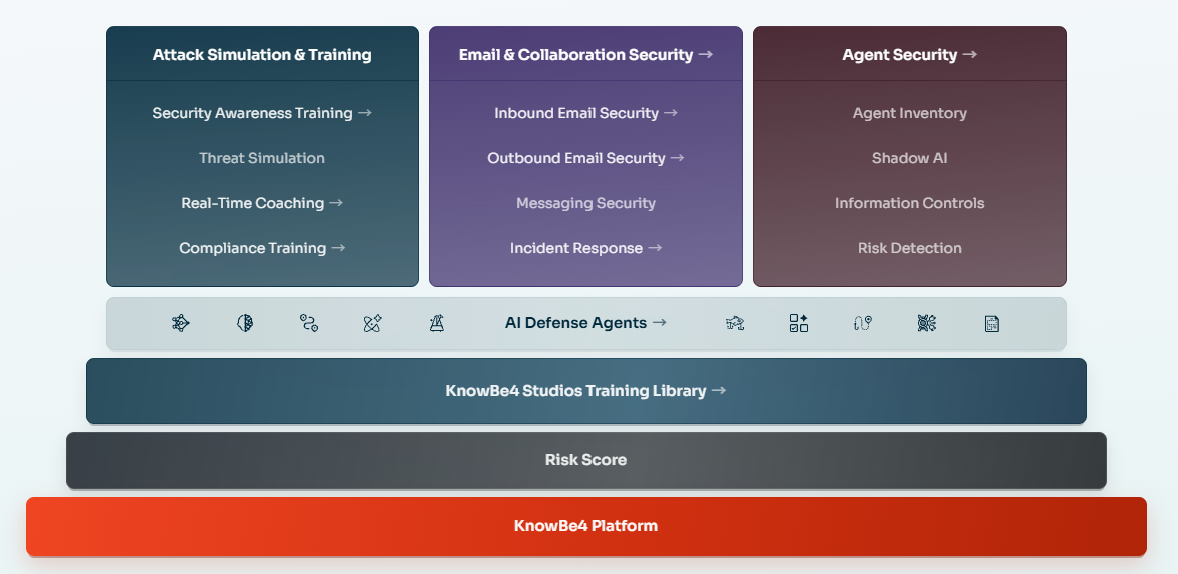
KnowBe4 helps organizations to incorporate human risk into their compliance system, so that assessments can be based on data and audits can be supported by evidence.

I. Article 24 "Risk Assessment" - Speaking with data, no more guessing

Conventional assessments often overlook the safety awareness of employees, resulting in risk gaps.
  • Baseline Testing: Prior to the assessment, a company-wide field test is conducted by simulating phishing emails (e.g. fake remittances, fake system notifications) to obtain a true Phish-prone Percentage.

  • Dynamic Rating: The system dynamically calculates risk scores based on employee clicking behavior, training completion and reporting rates.

  • Compliance Advantage: Translating the "likelihood of man-made threats" into quantifiable, real-world data satisfies the requirements of Section 24 for risk identification and continuous monitoring.

II: Article 25 "Security Audit" - Proving Controls Work in the Field

Auditors look not only at the documentation, but also at "whether the controls are actually working".
  • Ongoing Validation: Regular social engineering tests (weekly/monthly) are the best "control tests".
  • Complete Evidence Link: The system automatically records test content, click-through rate, report rate and improvement trend.
  • Compliance Advantage: Demonstrate to the auditor a dynamic, validated security management program, not just a static document with a signed acknowledgement.

Report automation - one-click export, save time and effort

The most time-consuming part of the annual assessment is the data integration, KnowBe4 provides 60+ report templates:

  • One-click export: Covers management dashboards, detailed risk assessments and departmental analysis in direct support of compliance documentation.

  • Legal shields: Complete training and testing records are the best legal weapon to prove that a business has "Due Diligence" (DD).

Client Side: Overall Improvement of Delivery Quality

Stable and consistent detection accuracy is a direct result:

  • Reduced return rate
  • Reduced risk of outflow of defective products

with respect to Regulatory, Medical The competitive advantage is particularly clear for customers with high standards.

Practical cases show that after importing Quarterly Rework Rate for a single production line of an HONGKE customer decreased by 0.8 percentage points.The overall yield rate has increased significantly.

KnowBe4 Helps to Address Compliance Challenges of Hong Kong's CISO Ordinance

KnowBe4 provides a simplified solution for enterprises to cope with the Hong Kong Critical Infrastructure Protection Ordinance (CIPO). Faced with the stringent challenges of Sections 24 and 25, KnowBe4 transforms the difficult-to-quantify "man-made risks" into traceable, real-world data that not only bridges the blind spots of traditional assessments, but also provides hard evidence of "effective operation" of controls for annual audits. Through automated reporting and continuous rehearsal, organizations can easily meet regulatory requirements while significantly reducing security risks, realizing the critical transition from "passive compliance" to "active defense.

Other Articles

Hongke Dry Goods

[Hongke Solutions] Human Security Defenses for Hong Kong Businesses: Compliance, Training, and AI-Powered Phishing Response – KnowBe4 Solutions

Generative AI phishing attacks are surging, and technical defenses alone are insufficient to counter social engineering. This article provides an in-depth analysis of the latest data from HKCERT, as well as key regulatory compliance requirements under the PDPO, HKMA CFI 2.0, and SFC. It also explains how to use KnowBe4 to establish a continuous human-factor risk management cycle and automated training exercises.
Read more
Hongke Dry Goods

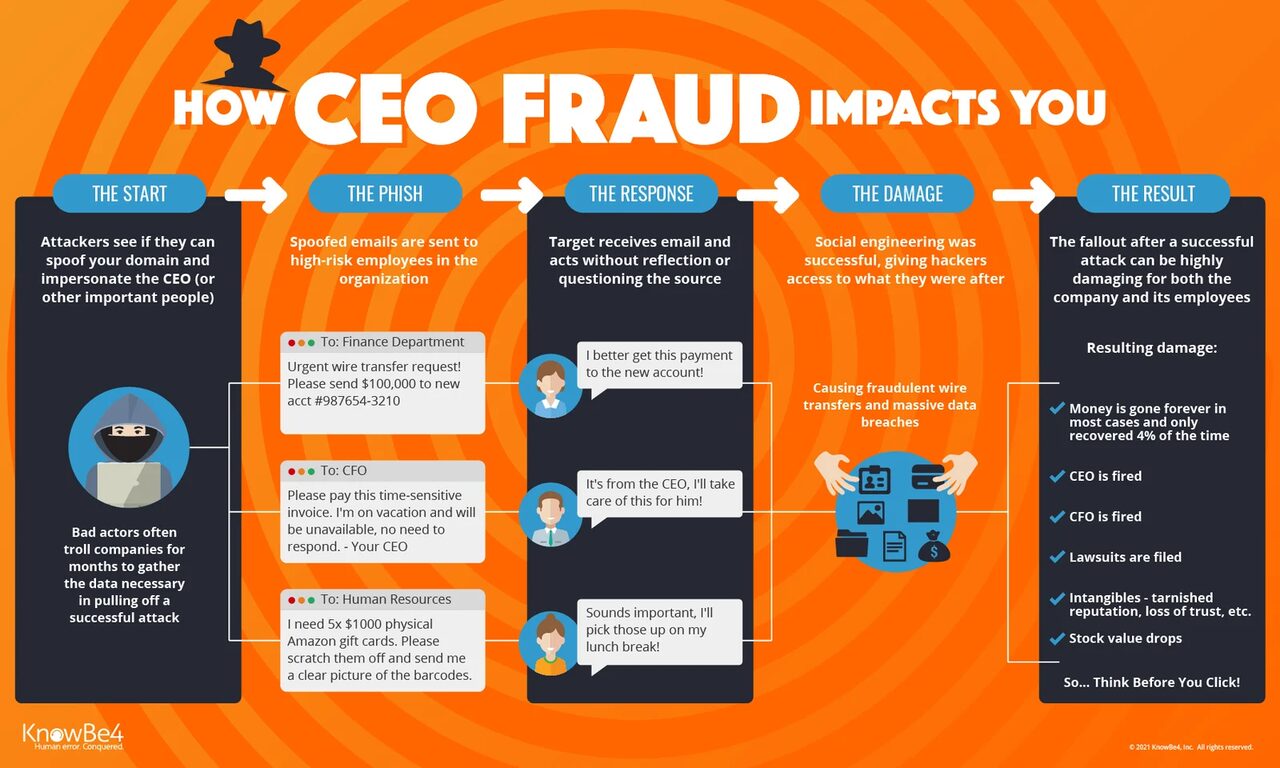
[Hongke Insights] Did You Receive an Urgent Email from the CEO Asking for a Wire Transfer? It Might Be a Scam: How Companies Can Protect Themselves Against Business Email Compromise Scams

An urgent email from the CEO requesting a wire transfer could be a Business Email Compromise (BEC) scam! Scammers impersonate the CEO, CFO, or a supplier and use their positional authority, along with urgent and confidential language, to trick employees into making wire transfers, changing bank accounts, or disclosing sensitive information. This article breaks down common CEO fraud tactics and shares prevention strategies for businesses, including KnowBe4-style security awareness training, simulation exercises, one-click reporting, independent payment verification, and dual approval processes—all designed to help organizations thwart these scams.

Read more
Hongke Dry Goods

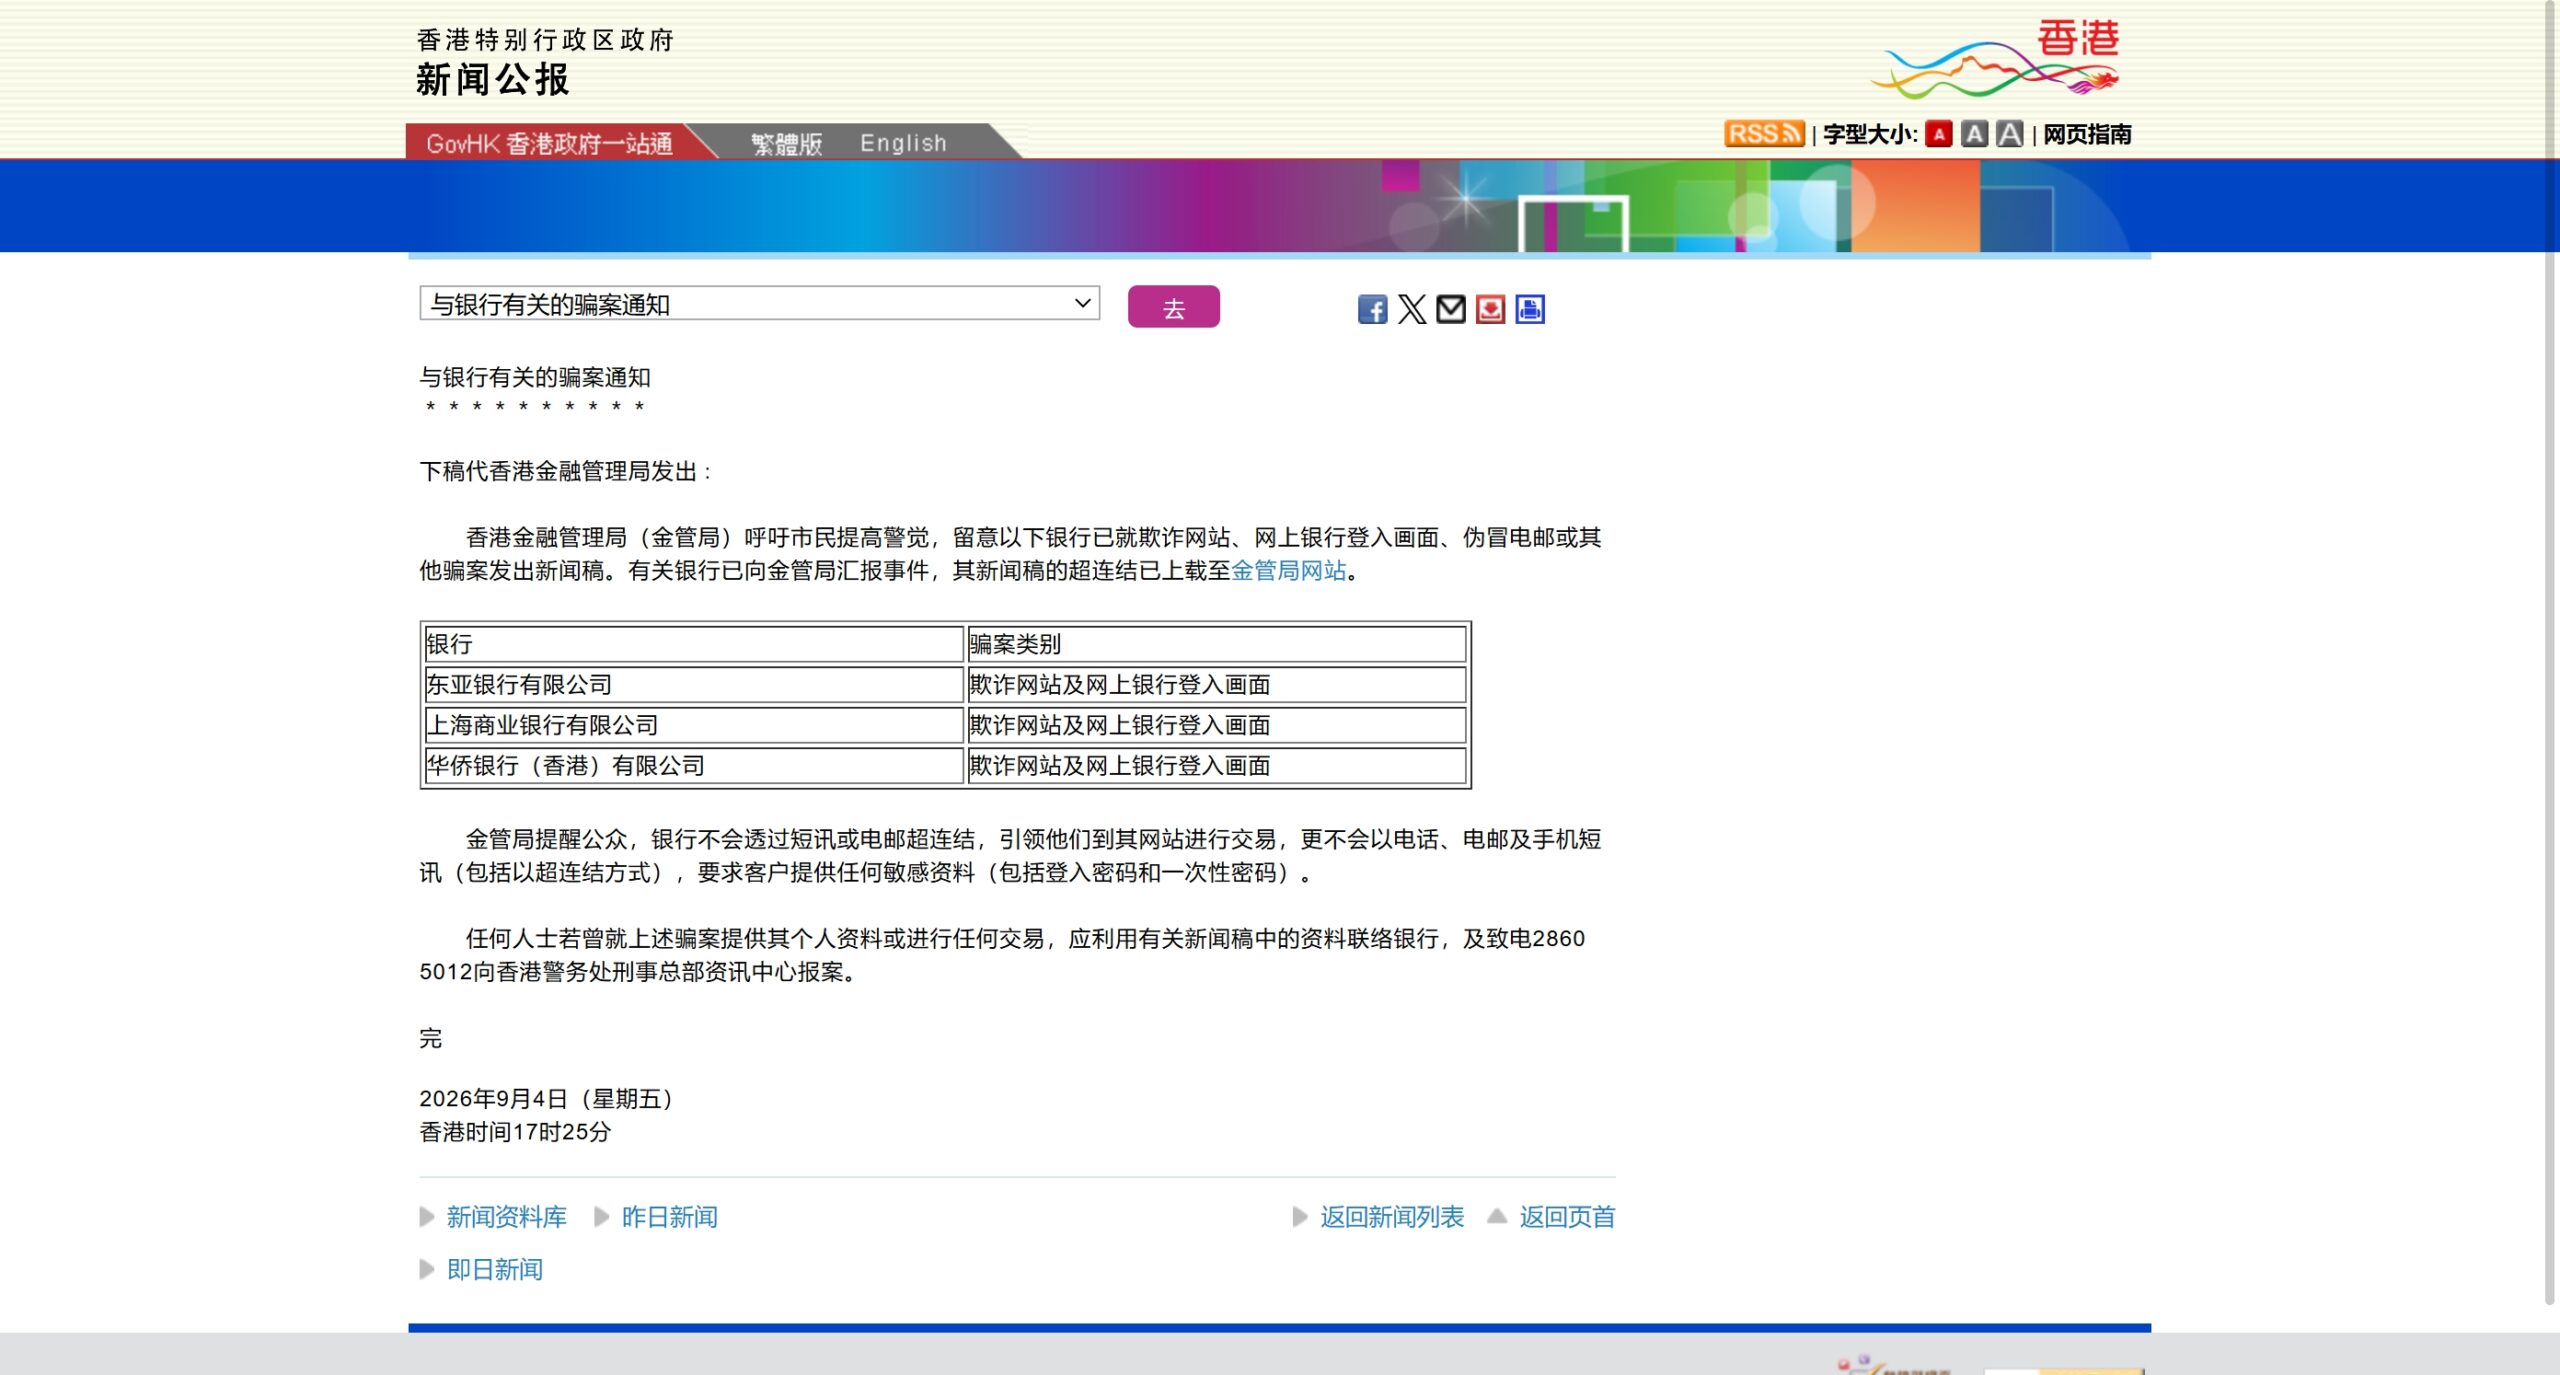
[Hongke Insights] The Hong Kong Monetary Authority’s Anti-Fraud Checklist Reveals Corporate Blind Spots: Why the Financial Industry Needs KnowBe4-Style Cybersecurity Awareness Training

The Hong Kong Monetary Authority’s “Beware of Scammers!” anti-fraud checklist is continuously updated, exposing scammers who impersonate banks and create fake websites, emails, and apps. Phishing attacks are becoming increasingly industrialized, and nearly all of Hong Kong’s major banks have been targeted by imposters. Relying solely on firewalls and email gateways makes it difficult to block social engineering attacks that bypass technical checks; what scammers truly exploit is people’s sense of urgency and trust. KnowBe4-style cybersecurity awareness training employs a closed-loop “assessment, training, simulation, feedback” approach. Through simulated phishing attacks, microlearning, real-time coaching, and quantifiable reports, it continuously enhances employee vigilance, transforming employees from the weakest link into the first line of defense.

Read more

Contact Hongke to help you solve your problems.

Let's have a chat