Search

Redis + Graph Database: Bank AML and Anti-fraud Real-Time Risk Control Architecture
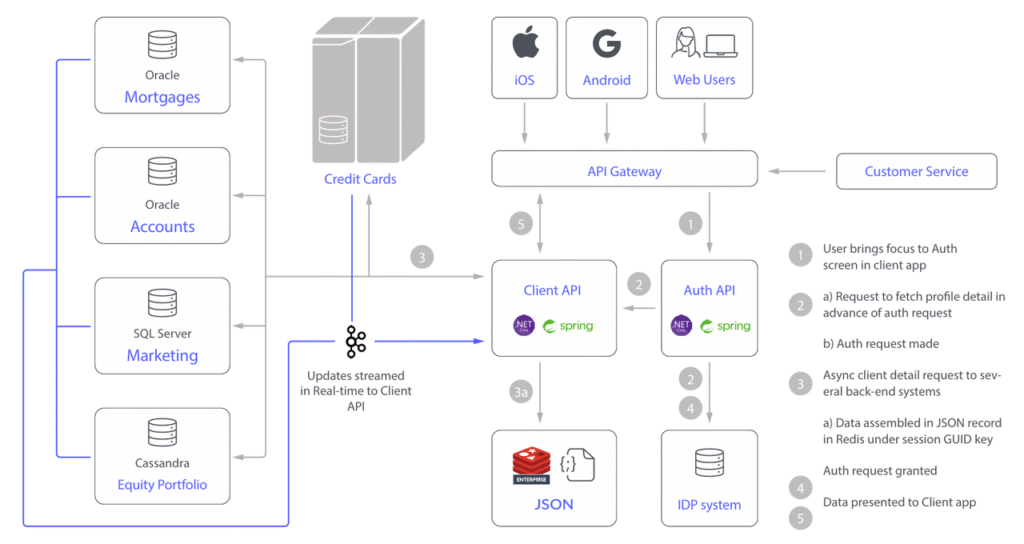
Banks dealing with AML and anti-fraud often face the tension between real-time decision-making and in-depth investigation. In this paper, we analyze how Redis (real-time scoring) and ArangoDB (graph database correlation analysis) can be perfectly divided into different roles and combined with Decisions to automate the process to meet the HKMA compliance guidelines and create a millisecond RegTech defense.

[HTC Expert Opinion] Why the mixing of "Linked Database + Graph Database" will push the system to the high complexity threshold?

Enterprises blindly mixing "federated databases + graph databases" often lead to a surge in system architecture complexity due to data consistency, fragmented ACID transaction boundaries, and cross-system splicing of application layers. HongKe brings you an in-depth look at the maintenance cost of Polyglot Persistence, and demystifies how multi-model DBs such as ArangoDB can reduce the hidden cost of enterprise IT with a "unified framework".

Hongke Solutions] Decision Automation vs Process Automation: Breaking the Bottleneck of B2B Digital Transformation

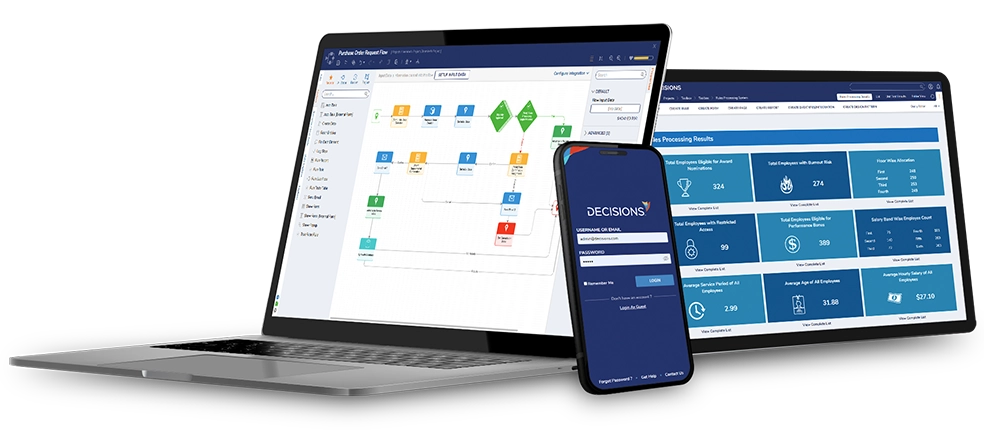
Just because a process is fast doesn't mean a decision is fast! HongKe explains how to systematize "decision logic" through the Decisions platform. From discount authorization to risk management, decision automation can dramatically improve consistency and compliance, helping Hong Kong and Southeast Asian companies achieve high-quality growth. Learn more about our automation upgrades today!

Hongke Solutions] Process ≠ Decision: The Most Often Ignored Technical Divide in Enterprise Digital Transformation Architecture

Process management is the foundation of enterprise digital transformation, but the technical positioning of process systems determines that they are incapable of undertaking complex decision-making functions. Embedding decision logic into processes not only leads to system bloat and maintenance difficulties, but also limits the extensibility of an enterprise's digital architecture.Decisions provides a practical solution to decouple processes and decisions through a standardized technical architecture, flexible rules management capabilities and seamless integration, helping enterprises create a simple, efficient and scalable digital architecture.

Rainbow Solutions] 2026 Procurement Committee Must-Have: Hong Kong Bank Redis Procurement Checklist (Open Source vs Enterprise Decision Framework)

The HKMA has repeatedly emphasized risk-based and principle-driven requirements in recent years, and has brought the risk of third-party IT solutions to the forefront, meaning that it's fine to turn on Maintenance or Redis Enterprise, but you have to prove that the "controls work" rather than that the "tool is famous".

HongKeys Solution] How to land CRA compliance? Network security engineer perspective to bring you to understand the logic of compliance and ONEKEY security and compliance platform value.

With the EU's Cyber Resilience Act (CRA) coming into force, product security and supply chain transparency have become mandatory requirements for companies entering the European market, with the CRA requiring manufacturers to establish security mechanisms throughout the entire product lifecycle and to provide SBOM, vulnerability management, and evidence of compliance. With the gradual implementation of the EU Cyber Resilience Act (CRA), product security and supply chain transparency has become a mandatory requirement for enterprises to enter the European market, and the CRA requires manufacturers to establish a security mechanism throughout the product lifecycle and provide SBOM, vulnerability management, and evidence of compliance. The ONEKEY Safety and Compliance Platform helps enterprises to quickly complete compliance diagnosis and vulnerability management, and establish a traceable and verifiable product safety and compliance system.

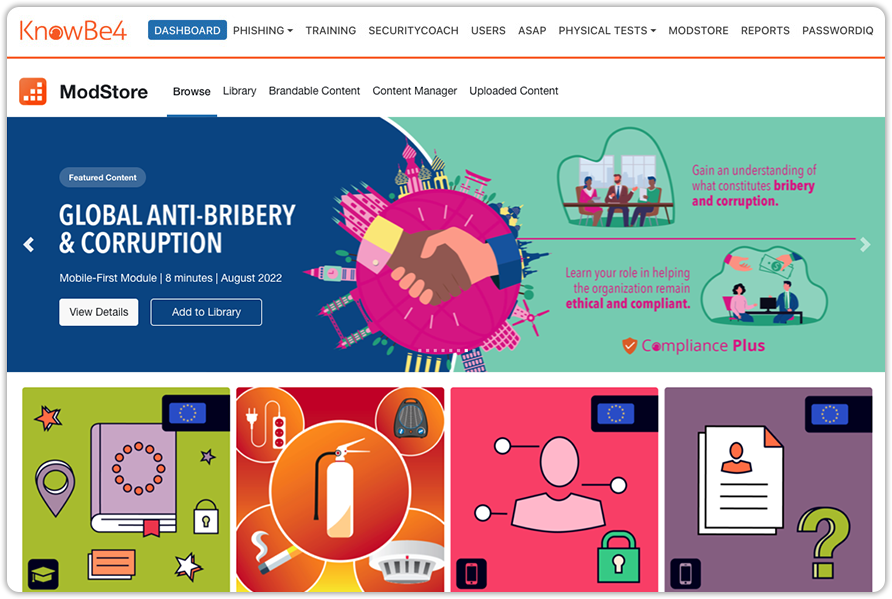
Hongke Solution] Making Compliance Training a "Quantifiable Line of Defense": Using KnowBe4 to Connect the Safety Awareness + Compliance Training Chain

In the context of digital transformation and increasing regulatory requirements, it is often difficult for enterprises to truly reduce human risk if they still manage compliance training and information security awareness training separately, KnowBe4 establishes a closed-loop management model of "test, train, retest, and data feedback" through simulated phishing tests, security awareness training, and the Compliance Plus compliance training library. Enterprises can integrate compliance courses and safety training into end-to-end training governance, and establish a quantifiable, traceable and auditable compliance training system.

[Hongke Solutions] EU AI Act: How AI Literacy Training for Enterprises can be Implemented

With the gradual implementation of the EU AI Act, AI governance is moving from corporate self-regulation to mandatory compliance. According to Article 4 of the Act, providers and users of AI systems must take measures to ensure that employees have adequate AI Literacy. Enterprises will need to translate AI knowledge into actionable compliance processes through tiered training systems, role-based curriculum design, and continuous tracking mechanisms.

From 60% to 5%: How Anglo-Eastern built a network security defense in a year's time

Anglo-Eastern Ship Management is a global ship management company managing more than 750 vessels. Faced with more than 32,000 seafarers around the world and the ever-increasing risk of cyberattacks, the company deployed the KnowBe4 HRM+ security awareness training platform to implement continuous employee cybersecurity education and simulated phishing tests. In just one year, the susceptibility rate to phishing attacks dropped from 60% to 5%, the training completion rate exceeded 90%, and employees proactively reported about 200 suspicious emails per day.

Hongke Solutions] Enterprise Mail Security from Crunchbase Leakage: How to Prevent Misdelivery and Sensitive Data Exfiltration?

In early 2026, Crunchbase confirmed a major data breach, proving once again that a single successful phishing attempt can result in hundreds of megabytes of file exfiltration. In addition to external attacks, organizations often overlook the risks of "misdirected mail" and internal outbound communications. This article analyzes the trend of phishing industry, compliance pressure (e.g., HIPAA, GDPR, GLBA), and provides a three-pronged protection strategy of integrated DLP, behavioral AI, and email encryption, which can help enterprises to stop the risk immediately before the data is sent.

Contact Hongke to help you solve your problems.

Let's have a chat