Search

Hongke's latest articles

HongKe

Lorem ipsum dolor sit amet, consectetur adipiscing elit. Ut elit tellus, luctus nec ullamcorper mattis, pulvinar dapibus leo.

[KnowBe4 Insights] 12-Hour Countdown: How Does KnowBe4 Turn Employees into Incident Early-Warning Radars?

Once the Critical Infrastructure (Computer Systems) Protection Ordinance (CISO) takes effect, the question will no longer be “whether you’ve implemented cybersecurity measures,” but rather “whether you can prove within the specified timeframe that you’ve identified the incident, are addressing it, and have reported it on time.” In particular, Section 28 imposes strict time limits for incident reporting: the specified timeframe for serious incidents can be as short as 12 hours, with an additional requirement to submit written records within 48 hours and to file a further written report within 14 days.

I. Introduction: The regulation is about to take effect; there are only 12 hours left to report the incident

The most common—and most devastating—way an incident begins is often not a zero-day exploit, but simply “a slip of the finger.” A payment reminder email impersonating a supplier, a delivery confirmation link impersonating a shipping company, or an urgent directive impersonating a supervisor—all it takes is a single click from an employee to trigger, within minutes, credential leaks, email account takeovers, and lateral movement, ultimately leading to a data breach or ransomware incident.
The problem is that many teams’ detection processes still rely solely on “waiting for SIEM/EDR alerts.” The later you “become aware” of an incident, the more brutal the notification deadline under Article 28 becomes: Schedule 6 sets “fixed deadlines” in stone: notifications for serious incidents must be completed within a minimum of 12 hours, and follow-up information must be submitted at intervals of 48 hours and 14 days.
For incident response (IR) and IT operations, the reality following the CISO’s appointment can be summed up in three words: race against time.

II. Three Core Values: How KnowBe4 Builds a Line of Defense Against Crises

Value #1: Turn "Every Inbox" into Your Early Warning Radar

The pain point is very real: Once a phishing email lands in the inbox, the SOC often has to wait until “someone falls for it” or “the suspicious behavior becomes obvious enough” before an alert is triggered.
KnowBe4’s Solution: KnowBe4’s Phish Alert Button (PAB) allows employees to safely forward suspicious emails to the security team for analysis with a single click, while simultaneously removing the email from the user’s inbox to prevent accidental clicks. This effectively turns the entire company’s workforce into a “network of sensors,” enabling the IR team to obtain firsthand samples before an incident spreads.
The effectiveness of the campaign:
  • Key Performance Indicator (KPI) (We recommend including this in your contingency plan): Reduce the time it takes for a “suspicious email to be reported to the SOC and a sample received” from the previous 30–60 minutes—which relied on manual forwarding—to 1–3 minutes (since employees only need to click a button, and the process no longer depends on memory or individual initiative).
  • More importantly, this ability to “know in advance” directly helps you gain a head start by moving the clock forward before the 12-hour notification countdown in Article 28 even begins.

Benefit 2: Automate “Categorization + Deletion” to Shorten the First Mile of IR

You’ve probably encountered this situation: A bunch of employees report suspicious emails, but the SOC ends up being flooded with false positives, causing the truly dangerous ones to be delayed.
KnowBe4’s Solution: PhishER automates the routing and prioritization of user-reported emails and provides capabilities such as PhishRIP to help quickly remove confirmed threats from inboxes, thereby reducing the risk of propagation. It can also integrate with PAB, enabling “employee reports” to be directly routed to “IR triage and resolution.”
The effectiveness of the campaign:
  • Reference KPI (we recommend including this in your exercise metrics): Reduce the “initial triage time per reported email” from 5–10 minutes of manual review to 1–2 minutes (by first using automated classification, with analysts handling only high-risk items).
  • Once it is confirmed that this is part of the same attack campaign, the goal is to reduce the time required to “clear identical malicious emails across mailboxes”—which previously took 1–2 hours (manual search plus individual processing)—to 10–20 minutes (with the aim of implementing an automated batch processing workflow).

Value 3: Put drills and emergency plans into practice—don’t just leave them on paper

The CISO doesn’t just want you to “know how to handle things”; they also want you to “conduct drills, have a plan, and be able to execute.” Section 26 of the Ordinance requires participation in computer system security drills, and Section 27 requires the submission and implementation of an emergency response plan; this means your IR runbook cannot simply be a document on Confluence—it must be repeatedly validated.
KnowBe4’s Solution: PAB lets you incorporate “employee reporting” into your emergency response plan and use the same set of tools to repeatedly run through the process during drills (who reports, when the SOC receives the report, how to triage, and how to notify). When integrated with PhishER, you can even turn real attacks into training material for future exercises (turning incidents into ammunition for the next drill), transforming security culture from mere slogans into a self-sustaining cycle.
The effectiveness of the campaign:
  • Reference KPI (suitable as a quarterly exercise goal): Raise the “reporting rate” (the percentage of recipients who are willing to click the report button after receiving a suspicious email) to 30% within 90 days, and to 50% within 6 months, ensuring that the SOC no longer relies solely on automated detection but also has a stable source of human-driven signals.
  • From a compliance perspective, it’s even more straightforward: your drill records, incident reports, and resolution records can all be used to piece together the content required for the 48-hour written record and the 14-day follow-up report under Article 28.

III. Conclusion: Take Action Now—Don’t Wait Until the Regulations Take Effect to “Catch Up”

What the CISO truly changes isn’t whether or not you “do cybersecurity,” but rather transforming incident response into a process that can be reviewed, held accountable, and timed. You now have only two options: passively wait and track the time after an incident occurs, or take a proactive approach to detect threats earlier and secure a lifeline within the 12-hour window.
The suggested next step is simple:
  • Schedule a 30-minute workshop to compare the reporting deadlines in Article 28 (12 hours/48 hours/14 days) with your existing processes and conduct a “countdown simulation.”
  • At the same time, launch a PAB pilot program (starting with the three high-risk departments: Finance, Procurement, and HR) and use the data reported within a week to directly quantify “whether you can gain early insight.”

Other Articles

Hongke Dry Goods

[Hongke Solutions] ArangoDB Contextual Data Platform: Key Architecture for Next-Generation Network Asset Management (CAM/CMDB)

An in-depth analysis of how enterprises can transition from single LLM API calls to autonomous agentic systems. This article compiles real-world examples of AI agent deployments in production environments across six major industries, including retail and finance, and breaks down the underlying infrastructure logic—such as high concurrency, cross-interaction memory (Memory Infrastructure), and distributed state persistence.
Read more
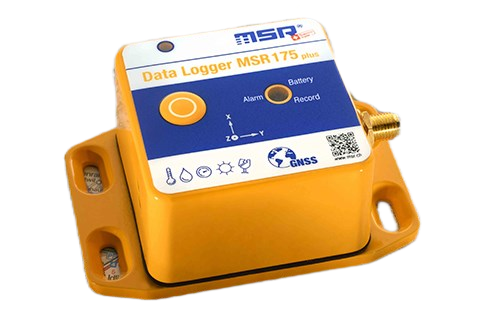
虹科 MSR175plus 衝擊與環境數據記錄器外觀圖:黃色堅固外殼配有 GNSS 定位功能、三軸加速度(X/Y/Z)以及溫度、濕度、氣壓、光照與傾斜感測器圖示,專用於運輸與物流監測。
Hongke Dry Goods

[Hongke Case Study] TSMC Selects MSR Shock and Vibration Data Loggers

How Can You Prevent Vibration Damage During International Transport of Semiconductor Wafers and Photomasks? We Reveal the Key Reasons TSMC Chose Hongke’s MSR175Plus Shock and Vibration Data Logger! The product features long battery life and large-capacity memory, enabling precise recording of temperature, humidity, pressure, and multi-axis acceleration during long-distance transport. In an exclusive interview, a TSMC engineer shares how the company converts vibration into quantifiable data and establishes rigorous standards to effectively reduce the risk of damage and significantly improve the success rate of international shipments!

Read more
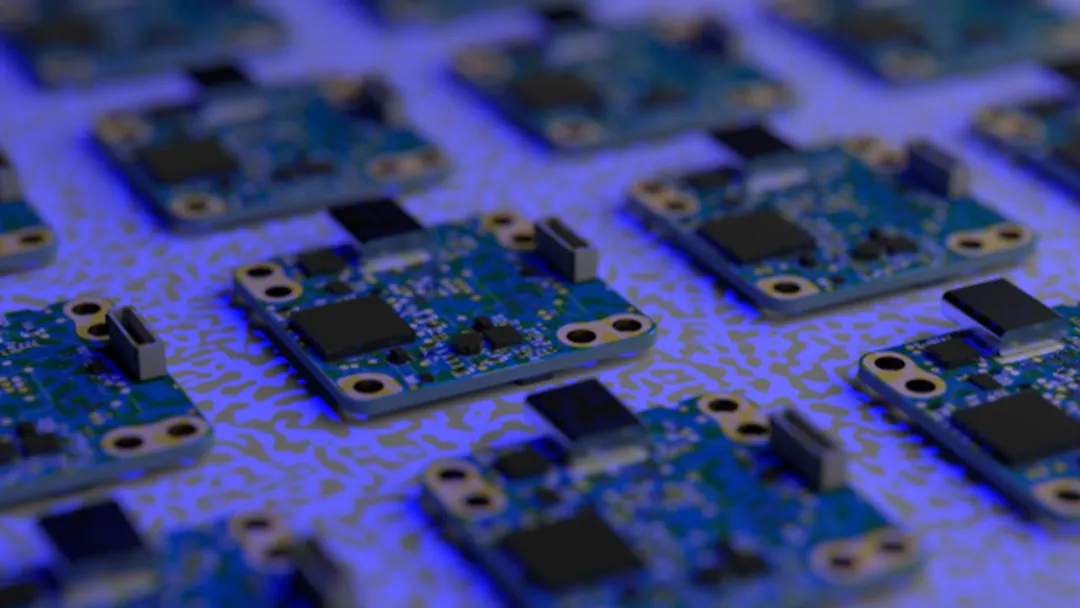
PCB 電路板組裝視覺檢測與測量示意圖:陣列排列的印刷電路板(PCBA)在藍光光源下展示晶片、元件與金屬焊盤細節,適用於 SMT 表面貼裝自動光學檢測(AOI)與品質管控。
Hongke Dry Goods

[Hongke Solutions] How Can AI-Powered Industrial Vision Inspection Overcome Quality Bottlenecks? A Comprehensive Analysis of Multi-Camera PTP Synchronization and Defect Detection

An In-Depth Analysis of AI Industrial Vision Inspection Technology! Explore how high-resolution industrial cameras, AI deep learning algorithms, and IEEE 1588 PTP microsecond-level multi-camera time synchronization precisely overcome bottlenecks in PCB component measurement and lithium-ion battery defect detection, and SMT Automated Optical Inspection (AOI), thereby improving production line yield!

Read more

Contact Hongke to help you solve your problems.

Let's have a chat