Search

Hongke's latest articles

HongKe

Lorem ipsum dolor sit amet, consectetur adipiscing elit. Ut elit tellus, luctus nec ullamcorper mattis, pulvinar dapibus leo.

Hongke Solution] Cracking the Ransom Dilemma: KnowBe4 Practical Guide to Build an Indestructible "People + Technology" Defense System

Highlights

Phishing attacks and ransomware are posing an ongoing threat to enterprise information security in a lower-cost, higher-revenue manner. From email baiting to double ransom, from vulnerability exploits to social engineering traps, traditional defenses are being challenged to the limit.
This article systematically comprehends the current threat landscape of enterprise cybersecurity, and details the role of enterprises in theMultifactor Authentication (MFA),Vulnerability Management,Cloud Backup,Mail Protectionbest practices in areas such as With a special focus on KnowBe4 How to do it throughSimulated Fishing Training,Behavioral AnalysisandSafety CultureIn order to create a "people"-focused security defense line, we help organizations to truly realize the "last mile" of information security.

Phishing and Ransomware: The Sword of Damocles in the Digital Society

Phishing Attacks: Social Engineering Tools for the Digital Age

Phishing is a typical social engineering attack that entices victims to provide sensitive information or perform malicious actions. Common methods include:

  • Fake links in emails or text messages

  • False Identity Interaction on Social Platforms

  • Create a sense of urgency by utilizing current events (e.g., epidemics, tax periods).

Most of them are aimed at account theft, malware implantation or subsequent ransom attacks.

Ransomware: Hackers' 'Commercialized Weapon'

Ransomware attacks are usually premised on infiltration, and common methods include:

  • Remote Desktop Protocol (RDP) configuration is not appropriate.

  • Malicious attachments to fishing emails

  • Software update channel hijacked

  • Social engineering induces the installation of malicious programs

Modern ransomware generally adopts the "double ransom" model:Encrypt the data, then threaten to leak it for a higher return.

Traditional Technology Defense: Six Security Strategies with "Technology" as the First Priority

Multi-Factor Authentication (MFA)

According to the White Paper survey, organizations in the 74% consider MFA to be one of the most effective techniques for preventing phishing attacks.
MFA upgrades the verification from "knowing something" (password) to "owning something" (device) or "being someone" (biometrics), dramatically reducing the risk of password theft, i.e., intrusion.

Suggested Prioritization:
FIDO2 Hardware Key > Biometrics > TOTP Application > SMS or Email Authentication Code

Security Awareness Training (SAT)

One of KnowBe4's core services is to help organizations build an "Employee Safety Immunity System".
Effective training should cover:

  • Tips for recognizing phishing emails, business email scams (BEC), and social engineering traps

  • Design simulation exercises for high-risk positions (e.g. finance, personnel)

  • Quantify employee response through periodic phishing tests to track improvement results.

Quick Bug Fixes and Virtual Patches

About 36% organizations were able to patch the vulnerability within hours after it was made public, but 20% took more than a couple of weeks, leaving hackers with an opportunity to exploit the vulnerability.
Businesses should be established:

  • Automated Patch Management System

  • Zero-Day Defense and Intrusion Prevention (IPS) capabilities

  • Isolation of legacy systems and application layer security protection

Mail Security and Identity Authentication (SPF/DKIM/DMARC)

Properly configured email validation mechanisms can effectively reduce domain spoofing and phishing emails. The best results are achieved when all three are used in conjunction:

  • SPF: Defining a Trusted Outgoing Mail Server

  • DKIM: Ensure that the contents of the email have not been tampered with

  • DMARC: Develop a strategy for suspicious mail (quarantine or reject)

Cloud Security and Endpoint Visualization

Cloud Security Demand Continues to Rise as Remote Work Gains Popularity. The White Paper shows:

  • More and more companies are deploying Cloud Native Security Services(e.g. CASB, EDR/XDR)

  • adopt AI/Machine Learning (ML) Automated detection and response

  • Through Hosted Security Services (MSSP) Responding to high-intensity attacks

Cloud Backup and Data Recovery Capabilities

More than 60% organizations consider offline or cloud backups to be a critical measure against ransomware.
Effective backup strategies should include:

  • Regular and complete data snapshots

  • Backups are stored offline to prevent simultaneous encryption.

  • Regular rehearsal of the recovery process to ensure RTO/RPO control

KnowBe4: Building an Enterprise Security Culture and Practical Combat Mechanism with a "People" Approach

As technological defenses become more sophisticated, attackers are beginning to exploit human weaknesses as a breakthrough.
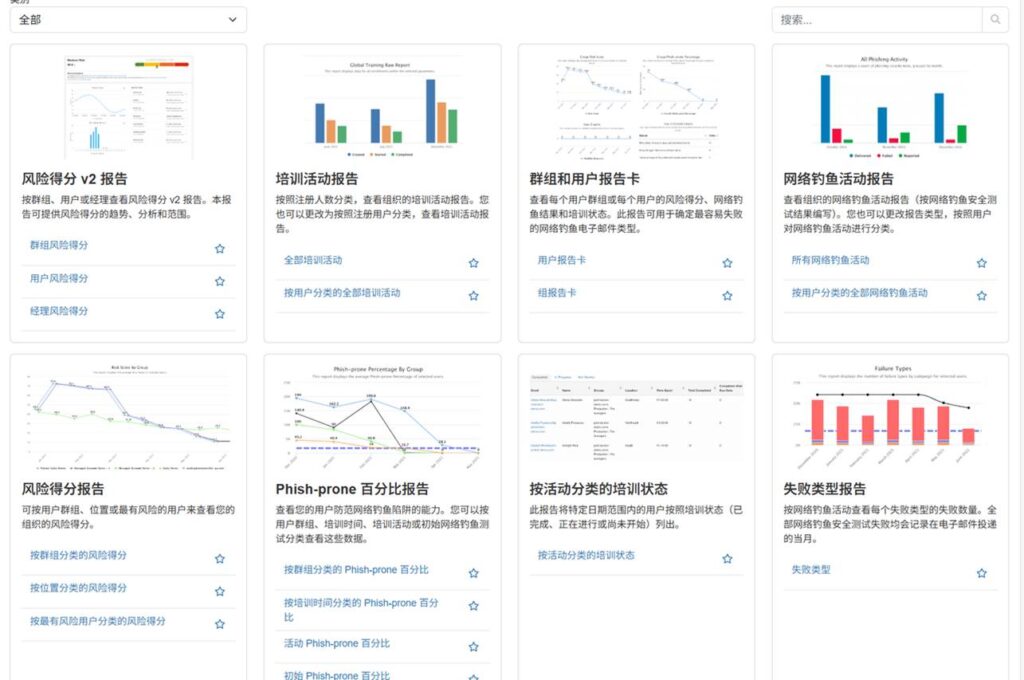
KnowBe4 Through the systematic "Security Awareness Training + Simulation Exercise" system, we help enterprises to enhance employees' defensive instincts, make up for the shortcomings of "human defense", and reduce the occurrence of phishing and extortion incidents from the source.

Core concepts:

  • Focus on the root cause and not the symptoms: Build a first line of defense, starting with email security and identity authentication.

  • Cultural orientation: Encourage employees to take the initiative to ask questions and develop a corporate culture of "everyone participates in safety".

  • human-machine collaborationThe concept of "People are the last line of defense", as advocated by KnowBe4, makes safety start from awareness.

  • Active testing and rehearsal: Early detection of vulnerabilities through red team simulations and phishing tests.

  • Preparedness: Establish a mechanism for collaborative planning with MSSP, law enforcement, and legal counsel.

Four key capabilities of KnowBe4:

  1. Real-world simulation training
    Provides the world's largest phishing email simulation platform, allowing employees to learn to recognize threats in a secure environment and quantify improvements through "click-through" data.

  2. Personalized Safety Training
    Designed for different positions (e.g. finance, HR, management), the specialized courses cover phishing prevention, ransom defense, password security and social engineering identification.

  3. Behavior-driven risk management
    The system creates a "risk profile" based on employee behavior (clicks, returns, completion) and automatically configures enhanced policies (e.g., mandatory MFA, permission control) for high-risk users.

  4. Safety Culture
    Through security tips, quarterly challenges and positive incentives, we are gradually fostering a culture of "everyone is responsible for security" to reduce the space for social engineering attacks.

IV. CONCLUSION

Phishing and ransom threats don't go away on their own, but continue to spread as attack thresholds are lowered and revenues are raised.
A New Type of Security Awareness Training by KnowBe4 It is the key to cracking the "human loophole".
By combining multi-factor authentication, automated detection, security culture building, and technological defense, enterprises can build a secure environment in an uncertain network environment.Firmware Defense SystemThe

Let security start with every employee, let defense become part of the corporate culture, and work with KnowBe4 to build an impenetrable "people + technology" information security line.

Other Articles

可配置的CAN FD模擬I/O模塊 功能概述: PCAN-MicroMod FD系列模塊是支持CAN FD的數采模塊。 PCAN-MicroMod FD 插入式板卡可以和即插即用的母板一起購買,母板提供了各種外設可滿足特定需要。對於CAN連接、I/O、和供電,可用彈簧端子連接器。 PCAN-MicroMod FD 數字版1和2著重於數字輸入和輸出,其上有相應的保護電路。數字1的數字輸出裝備了低邊開關,數字2的裝備了高邊開關。
Hongke Dry Goods

[Hongke Solutions] Can’t Read CAN Data? Not Enough Temperature Channels? A Comprehensive Guide to Integrating NVH and Battery Data Acquisition

Is your current NVH data logger unable to read the CAN bus? Are there not enough temperature channels for battery testing? Hongke offers the PCAN-MicroMod FD and MU-Thermocouple1 CAN FD modules to enable CAN(FD)-to-analog conversion and high-density thermocouple multi-module cascading expansion. No coding required—just unbox and use it right away, with no need to replace your existing system!

Read more
Hongke Dry Goods

[Hongke Solutions] AI Agent Implementation Case Study: Enterprise-Level Deployment Across Six Major Industries and the Logic Behind the Underlying Infrastructure

An in-depth analysis of how enterprises can transition from single LLM API calls to autonomous agentic systems. This article compiles real-world examples of AI agent deployments in production environments across six major industries, including retail and finance, and breaks down the underlying infrastructure logic—such as high concurrency, cross-interaction memory (Memory Infrastructure), and distributed state persistence.

Read more
Hongke Dry Goods

HONGKE SOLUTIONS] The Effect of Gaussian Noise on Positioning Effect in GNSS Simulation

In Global Navigation Satellite System (GNSS) radio frequency simulation testing, Gaussian white noise (AWGN) is typically regarded as the baseline configuration for replicating real-world electromagnetic environments. However, engineering practice has shown that the impact of noise on a receiver’s positioning performance does not follow a linear, monotonic relationship. Based on actual measurement data from the DST GNSS simulator, this paper analyzes the physical mechanisms of Gaussian noise in Kalman filters, correlator jitter, and phase-locked loops, and provides a scientific testing guide for configuring simulation noise.

Read more

Contact Hongke to help you solve your problems.

Let's have a chat